


ISO/IEC 27701:2025 Ushers in a New Era of Global Privacy Management
By Anil P. Kastuar, Editor, IBG NEWS
Kolkata | IBG NEWS Desk
As organizations worldwide face increasing scrutiny over the protection of personal data, the release of ISO/IEC 27701:2025 marks a significant advancement in global privacy governance. The newly published standard replaces ISO/IEC 27701:2019 and introduces a more comprehensive, flexible, and internationally aligned framework for establishing and managing Privacy Information Management Systems (PIMS).
With data privacy now recognized as a strategic business priority rather than merely a compliance requirement, the revised standard is expected to help organizations strengthen accountability, improve customer trust, and meet the demands of evolving privacy regulations across multiple jurisdictions.
A Stronger Foundation for Privacy Governance
ISO/IEC 27701:2025 provides organizations acting as both Personally Identifiable Information (PII) Controllers and PII Processors with a structured framework to establish, implement, maintain, and continually improve their Privacy Information Management Systems.
The updated standard supports compliance with major international privacy laws, including the European Union’s General Data Protection Regulation (GDPR), India’s Digital Personal Data Protection Act (DPDPA), the California Consumer Privacy Act (CCPA), Brazil’s Lei Geral de Proteção de Dados (LGPD), and other emerging global privacy regulations.
Major Enhancements in ISO/IEC 27701:2025
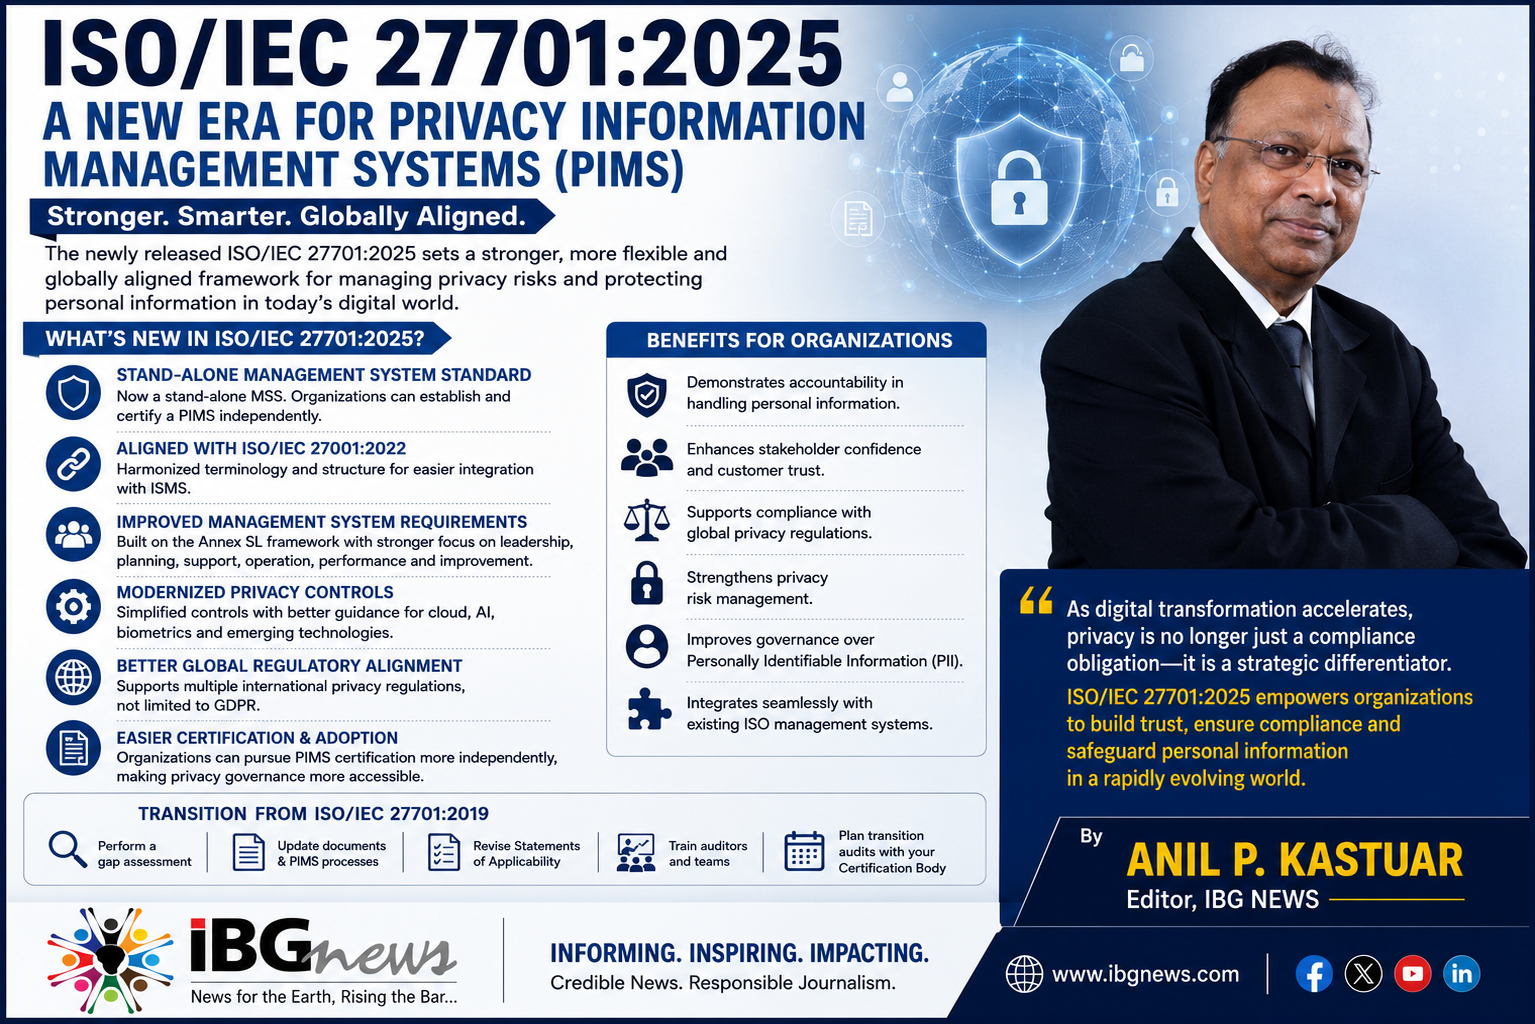
One of the most notable changes is that ISO/IEC 27701:2025 has evolved into a stand-alone Management System Standard (MSS). Unlike the 2019 edition, organizations can now establish and obtain certification for a Privacy Information Management System independently, without treating it solely as an extension of ISO/IEC 27001.
The revised standard has also been fully aligned with ISO/IEC 27001:2022 and ISO/IEC 27002:2022, ensuring consistent terminology, structure, and easier integration for organizations already operating Information Security Management Systems (ISMS).
Privacy governance requirements now follow the internationally recognized Annex SL management system framework, placing greater emphasis on leadership commitment, organizational context, strategic planning, operational control, performance evaluation, and continual improvement.
Modern Privacy Controls for Emerging Technologies
Recognizing the rapid evolution of digital technologies, ISO/IEC 27701:2025 introduces reorganized and simplified privacy controls that address contemporary challenges, including:
- Cloud computing environments
- Artificial Intelligence (AI)-enabled data processing
- Biometric information management
- Other emerging technologies with privacy implications
The revised framework also adopts a broader international perspective, making it suitable for multinational organizations seeking compliance across multiple regulatory environments rather than focusing predominantly on GDPR.
Key Benefits for Organizations
Organizations adopting ISO/IEC 27701:2025 can expect several strategic advantages, including:
- Demonstrating accountability in handling personal information.
- Enhancing customer confidence and stakeholder trust.
- Supporting compliance with international privacy regulations.
- Strengthening privacy risk management practices.
- Improving governance over Personally Identifiable Information (PII).
- Seamlessly integrating privacy management with existing ISO management systems.
Transition from ISO/IEC 27701:2019
Organizations already certified under the 2019 version should begin preparing for migration to the updated standard. Recommended transition activities include:
- Conducting a comprehensive gap assessment.
- Updating documented policies and Privacy Information Management System processes.
- Reviewing and revising Statements of Applicability where necessary.
- Providing training for internal auditors and implementation teams.
- Coordinating transition audits with accredited certification bodies.
Privacy as a Strategic Business Asset
As digital transformation accelerates across industries, privacy has emerged as a critical factor influencing customer confidence, corporate reputation, and regulatory compliance.
ISO/IEC 27701:2025 reflects this shift by providing organizations with a stronger, more adaptable, and globally harmonized framework for managing privacy risks while safeguarding personal information.
For businesses operating in an increasingly data-driven world, implementing the revised standard is no longer just about regulatory compliance—it represents a strategic investment in trust, resilience, and sustainable governance.

