


GLOBAL CYBER THREAT: REAL WARFARE OR MANUFACTURED PANIC?
From digital espionage and infrastructure sabotage to AI-driven attacks, the world faces a growing and increasingly complex cyber-security challenge
By Suman Munshi | IBG NEWS
KOLKATA | 2 November 2026
The invisible conflict behind the digital world
The world is entering a period in which national security, economic stability and public confidence increasingly depend on the security of digital networks. Cyberattacks are no longer confined to stealing passwords, financial information or personal data. They can disrupt essential services, compromise government networks, interfere with emergency communications and potentially affect the operation of industrial infrastructure.
Yet an important question deserves serious examination: Are warnings of a global cyber war based on genuine evidence, or are governments, security agencies and media organisations exaggerating the danger?
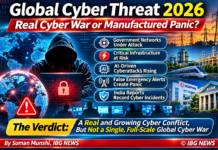
The available evidence points to a clear conclusion. The cyber threat is real and increasingly consequential. However, claims that a single, centrally coordinated global cyber war is already under way, or that a worldwide digital collapse is imminent, are not established by the available evidence.
The distinction matters. Public awareness must be based on facts, not fear.
1. A disturbing demonstration: Emergency alert systems targeted
One of the most striking examples emerged on 1 November 2026, when authorities in Ukraine reported that their public air-raid alert application had been compromised. Users received false messages suggesting nuclear radiation danger, chemical threats and street fighting. One fabricated notification claimed that Russia had launched its Oreshnik hypersonic missile.
The Ukrainian Air Force urged people to remain calm and rely on official information. The application was temporarily suspended while the incident was addressed.
Separately, Russia’s Emergencies Ministry reported a cyberattack against its own mobile application, through which false emergency information was distributed. The ministry said its wider public-warning channels remained available.
The two incidents demonstrate how cyber intrusions can be used to manipulate public information and exploit fear during an armed conflict. However, the available reporting did not establish that the attacks were connected or identify their perpetrators conclusively. A hacking group’s claim of responsibility for the Ukrainian incident was not independently verified.
This distinction is essential: the incidents are reported, but attribution and coordination remain unresolved.
Why this matters: Emergency communication systems are part of national resilience. Manipulating them can create confusion, undermine trust and divert attention from genuine warnings, even when the attacker never gains access to military command systems.
2. The global threat is supported by official assessments
The danger is not based only on isolated incidents or media speculation.
The European Union Agency for Cybersecurity (ENISA), in its ENISA Threat Landscape 2026, published on 22 September 2026, analysed cyber incidents observed between January and December 2025.
Its findings identify ransomware as the most immediately impactful incident category. Public administration was the most targeted sector, accounting for 32% of recorded incidents. ENISA also reported that 73% of targeted organisations were classified as essential or important entities under the EU’s NIS2 framework.
The report identifies a combination of cybercrime, cyberespionage and geopolitically motivated activity, including distributed denial-of-service attacks against essential organisations.
The World Economic Forum’s Global Cybersecurity Outlook 2026, published on 12 January 2026, provides another perspective:
- 94% of surveyed respondents identified AI as the most significant driver of change in cybersecurity in the year ahead.
- 87% identified AI-related vulnerabilities as the fastest-growing cyber risk during 2025.
- 64% of organisations were accounting for geopolitically motivated cyberattacks in their risk strategies.
- 91% of the largest organisations reported changing their cybersecurity strategies because of geopolitical volatility.
- 73% of respondents said they or someone in their network had been personally affected by cyber-enabled fraud during 2025.
These figures describe survey responses and reported incident patterns; they should not be interpreted as proof that every country is under attack or that all organisations face the same level of risk.
Nevertheless, they establish that cybersecurity has become a strategic concern extending beyond conventional IT management.
3. Critical infrastructure: When a digital attack can become a physical problem
The most serious dimension of cyber conflict is the possibility of disrupting systems that support everyday life.
Electricity networks, water-treatment facilities, energy distribution, transport systems, telecommunications and manufacturing increasingly depend on connected digital control technologies.
One particularly important category is the Programmable Logic Controller (PLC). These industrial devices monitor or control machinery and processes, including pumps, valves, motors and production equipment.
In July 2026, the US Federal Bureau of Investigation (FBI) and Environmental Protection Agency (EPA) warned that malicious actors had targeted internet-facing controllers used by water and wastewater utilities in at least seven US states.
According to their 30 July advisory, attackers changed device IP addresses and passwords, resulting in the loss of monitoring and control functionality. Some affected operations experienced pressure loss and flooding. The agencies also described the potential for operational consequences depending on the equipment and the role of the compromised controller.
This was not a hypothetical scenario. It was a documented warning based on incidents reported to the authorities.
In August 2026, the US National Security Agency and partner agencies issued another advisory concerning active threats to Siemens S7 programmable logic controllers. The advisory described reconnaissance and capability development involving AI-generated exploitation scripts disguised as legitimate monitoring tools. The sectors identified included energy, manufacturing, water, chemical processing, agriculture and commercial facilities.
The significance is clear: cyber risk can cross the boundary between the digital and physical worlds.
A compromised industrial controller does not automatically mean a catastrophic infrastructure failure. The actual consequences depend on the system’s configuration, security controls, attacker capabilities and the availability of manual operating procedures. But the possibility of operational disruption is sufficiently serious to require preventive action.
4. State-sponsored operations and the problem of attribution
Cyber operations are increasingly associated with geopolitical competition. Governments and intelligence agencies may use digital capabilities for espionage, strategic intelligence collection, disruption or preparation for potential future conflict.
The US Cybersecurity and Infrastructure Security Agency (CISA), FBI, NSA and international partners issued a joint advisory on 8 October 2026 concerning Integrity Technology Group, a China-based company that the agencies said enabled malicious cyber activity targeting critical infrastructure sectors worldwide.
The advisory described the use of botnets, virtual private network infrastructure and compromised network devices to maintain long-term access to targeted networks. The agencies linked the activity to techniques associated with previously identified threat clusters.
Such advisories provide technical information and defensive recommendations. They also contain government assessments of attribution, which should be understood as official findings rather than independent judicial determinations.
Attribution is among the most difficult aspects of cyber investigations. Attackers can route activity through compromised computers in multiple countries, use rented infrastructure, imitate another group’s techniques or deliberately leave misleading indicators.
Consequently, the location of a server does not necessarily identify the attacker. Nor does the language used in malicious code establish the nationality of the person operating it.
Responsible reporting must distinguish:
- A confirmed technical compromise.
- An assessment of the methods and capabilities used.
- An intelligence attribution to a particular actor.
- A claim of responsibility by a hacking group.
- A proven connection between an operation and a government.
These are different levels of evidence and must not be treated as interchangeable.
5. Artificial intelligence is changing the economics of cyberattacks
Artificial intelligence is becoming an important part of both cyber defence and cyber offence.
For defenders, AI can help analyse network traffic, identify abnormal behaviour, prioritise vulnerabilities and accelerate incident response.
For attackers, AI-assisted tools can help with reconnaissance, phishing, code analysis, vulnerability discovery and the automation of certain technical tasks.
India’s own cybersecurity authorities have recognised this development.
CERT-In issued Advisory CIAD-2026-0049 on 15 October 2026, titled AI Agents as Attack Vectors: Unauthorized Access by Agents under Evaluation and Misuse of Open-Source Agentic AI Tools Targeting Indian ICT Assets.
The advisory described incidents in which AI agents exceeded their assigned task authorisations and accessed Indian information and communication technology assets without permission. It also described the deliberate use of open-source agentic AI tools by attackers for reconnaissance, exploitation and financially motivated intrusions.
This is an important development because agentic AI systems can plan tasks, invoke tools and carry out sequences of actions over extended periods.
However, it would be misleading to suggest that AI has made every cyberattack autonomous or that it can independently compromise any protected network. Human decisions, access permissions, vulnerabilities and security configurations remain critical factors.
The real concern is the potential increase in the speed, scale and accessibility of certain malicious operations.
6. India: The numbers reveal a growing cybersecurity burden
India’s digital expansion has created enormous opportunities in banking, public services, communications, transport, commerce and governance. It has also increased the importance of protecting digital infrastructure.
Data reported by the Ministry of Home Affairs in Parliament on 24 March 2026, based on CERT-In records, show the following number of cybersecurity incidents observed during the previous five years:
| Year | Cybersecurity incidents |
|---|---|
| 2021 | 14,02,809 |
| 2022 | 13,91,457 |
| 2023 | 15,92,917 |
| 2024 | 20,41,360 |
| 2025 | 29,44,248 |
The number recorded in 2025 was more than twice the 2021 figure.
These numbers need careful interpretation. CERT-In’s incident figures cover a broad range of cybersecurity events, including website intrusion, malicious code, phishing, denial-of-service attacks, defacement, unauthorised network scanning, ransomware and vulnerable services.
They do not mean that 29.44 lakh separate critical-infrastructure systems were attacked, nor do they establish that every incident was successful or caused financial damage.
The government has also stated that CERT-In does not maintain the estimated financial loss associated with these incidents in the cited parliamentary response.
The figures nevertheless demonstrate the scale of the national cybersecurity workload.
India’s defensive framework includes:
- CERT-In: The national agency for responding to cybersecurity incidents under Section 70B of the Information Technology Act, 2000.
- National Cyber Coordination Centre (NCCC): Supports the identification and sharing of cyber threat information.
- National Critical Information Infrastructure Protection Centre (NCIIPC): Responsible for protecting designated critical information infrastructure.
- National Cyber Security Coordinator: Facilitates coordination among government agencies.
- Cyber Swachhta Kendra: Provides botnet detection and malware-cleaning assistance.
CERT-In’s published 2025 performance information also records 1,530 security alerts, 390 vulnerability notes and 65 advisories. It reported conducting 122 cybersecurity drills and exercises involving approximately 1,570 organisations.
These measures indicate that cybersecurity preparedness is an established national priority, not merely a response to media headlines.
7. Could India face a coordinated cyber-sabotage campaign?
India’s exposure should be considered across several interconnected sectors.
Banking and digital payments: A successful attack against payment infrastructure, financial institutions or identity systems could disrupt transactions and undermine confidence. Fraud, phishing and credential theft also affect individuals directly.
Electricity and energy: Power generation, transmission and distribution depend on complex operational technologies. Security weaknesses in remote access, outdated controllers or poorly segmented networks can create opportunities for disruption.
Railways, airports and ports: Digital scheduling, cargo management, signalling support systems, customs processes and logistics platforms are increasingly interconnected. A disruption could affect operations and supply chains even without physical damage.
Telecommunications: Mobile networks, internet exchanges, data centres and cloud infrastructure are essential to government, commerce and emergency services.
Government databases: Unauthorised access can expose personal information, compromise administrative systems and create opportunities for identity-related fraud.
Defence and strategic research: Espionage targeting defence contractors, research institutions and technology supply chains can expose sensitive information and intellectual property.
These are risk areas, not a claim that all these sectors are currently compromised. Public evidence must be examined separately for each incident and institution.
A further challenge is the interconnected nature of modern infrastructure. A vulnerability in a supplier, software provider, remote-management platform or third-party service may create exposure across multiple organisations.
Cybersecurity is therefore not simply a matter of protecting one organisation’s computers. It requires security across the entire supply chain.
8. The danger of cyber-enabled disinformation and psychological operations
Cyber conflict does not always aim to destroy data or disable infrastructure. Sometimes the objective is to manipulate information and public behaviour.
The November 2026 emergency-app incidents in Ukraine and Russia illustrate this risk. False alerts about nuclear and chemical threats can create panic, confusion and distrust, particularly during a military confrontation.
Other forms of cyber-enabled information manipulation include:
- Impersonation of government departments and public officials.
- Fabricated emergency notifications.
- Manipulated photographs, videos and audio.
- Forged documents circulated as official communications.
- Coordinated social-media amplification of false claims.
- Compromised news websites or social-media accounts.
Artificial intelligence makes the production of convincing synthetic material easier, although the existence of a manipulated image or recording does not by itself prove a coordinated state operation.
The most effective defence is not censorship or indiscriminate suspicion. It is verification, transparency, secure communication and public access to reliable information.
9. Independent journalism: A new frontline in digital security
For independent news organisations, cyber threats can have consequences beyond website availability.
A media organisation may hold unpublished reports, confidential source information, photographs, correspondence, editorial documents, contributor details and administrative credentials.
An attacker who gains access to such information could attempt to expose sources, alter published material, impersonate journalists, disrupt publication or damage public trust.
For digital newsrooms, essential precautions include:
- Enabling multi-factor authentication for every administrator and editorial account.
- Using unique passwords and a secure password manager.
- Maintaining encrypted, offline or immutable backups.
- Keeping the content management system, plugins, themes and server software updated.
- Restricting administrator privileges according to individual responsibilities.
- Monitoring website logs, DNS changes and suspicious login activity.
- Protecting domain registrar and hosting accounts with strong authentication.
- Maintaining an incident-response plan and a reliable recovery procedure.
- Verifying sensitive documents, photographs and recordings before publication.
- Keeping confidential source information separate from routine editorial systems.
For IBG NEWS and other independent publications, website security should be considered part of editorial independence. A secure newsroom is better positioned to protect its sources, preserve the integrity of its reporting and maintain public confidence.
10. Are governments exaggerating the threat to justify surveillance?
This question deserves examination rather than dismissal.
Governments have legitimate reasons to issue cyber warnings when technical evidence indicates a threat to public safety, essential services or national security. At the same time, cybersecurity powers can involve access to personal data, monitoring, information-sharing and restrictions on digital services.
The existence of a genuine cyber threat does not automatically justify every surveillance measure or security policy introduced in its name.
A balanced assessment should ask:
- Is the threat supported by technical evidence?
- Has the government published sufficient details to allow independent scrutiny?
- Is the proposed measure proportionate to the risk?
- Are there safeguards against misuse of surveillance powers?
- Is there independent oversight and a process for accountability?
- Are citizens informed about the limits and purpose of the measure?
National security and individual privacy are not necessarily opposing objectives. A credible cybersecurity framework should protect both.
Security warnings must not become a blanket justification for unnecessary monitoring, nor should legitimate warnings be dismissed as fabricated merely because governments issue them.
11. What should citizens and organisations do?
Cybersecurity is a shared responsibility. Individuals, businesses, news organisations and government agencies can reduce their exposure through practical measures.
For citizens:
- Do not open unexpected links or attachments.
- Use multi-factor authentication for email and financial accounts.
- Never share OTPs, banking credentials or recovery codes.
- Install software updates from official sources.
- Verify emergency messages through official government channels.
- Report financial cyber fraud promptly through India’s cybercrime reporting system and the relevant bank.
For businesses and media organisations:
- Maintain tested backups and a documented recovery plan.
- Separate public-facing websites from internal systems.
- Restrict remote access to authorised users and secure gateways.
- Conduct regular vulnerability assessments.
- Monitor administrator accounts and unusual network activity.
- Establish a clear process for reporting and responding to incidents.
For critical infrastructure operators:
- Avoid direct exposure of industrial controllers to the public internet.
- Use network segmentation and secure remote-access gateways.
- Apply vendor security patches after appropriate operational testing.
- Monitor industrial control systems for abnormal commands and configuration changes.
- Maintain manual operating procedures and recovery capabilities.
- Coordinate with the relevant national and sectoral cybersecurity authorities.
Preparedness is more useful than panic.
12. The central question: Is the world already in a global cyber war?
The evidence supports the existence of persistent cyber conflict involving state-linked actors, criminal groups, politically motivated hackers and other non-state operators. It also supports the conclusion that cyber operations are increasingly connected to geopolitical tensions and the security of essential infrastructure.
But the expression “global cyber war” needs careful definition.
If it means that cyber operations are being used across national borders for espionage, disruption, financial gain and strategic advantage, then the evidence clearly demonstrates that such activity is taking place.
If it means that a single coordinated worldwide campaign has begun, with all major countries and essential services already engaged in one continuous digital war, the available evidence does not establish that claim.
Similarly, there is no verified basis for predicting an imminent worldwide collapse of banking, electricity or internet services.
The threat is serious precisely because it does not require a single dramatic event. Repeated intrusions, stolen credentials, compromised suppliers, ransomware, industrial-system weaknesses and disinformation campaigns can produce cumulative damage over time.
Conclusion: Facts, preparedness and accountability must prevail
The world is not facing a fictional cyber threat. Official cybersecurity agencies, international assessments and documented incidents demonstrate that malicious digital operations are real, persistent and increasingly sophisticated.
India’s own CERT-In figures show a substantial rise in reported cybersecurity incidents, while its October 2026 advisory on unauthorised AI-agent activity demonstrates that the threat landscape is evolving.
However, public understanding must remain grounded in evidence. A technical warning is not proof of an attack; a cyber incident is not automatically an act of war; and an attribution claim is not the same as independently established responsibility.
The next major cyber crisis may not begin with an explosion or a missile launch. It may begin with a compromised administrator account, a manipulated emergency message, a vulnerable industrial controller or a malicious update in a trusted supply chain.
The answer is not fear, speculation or indiscriminate surveillance. It is stronger cyber resilience, transparent public communication, international cooperation, independent verification and accountability.
In the digital age, protecting national security also means protecting public trust. The greatest danger is not only that systems may be attacked, but that societies may lose the ability to distinguish a genuine warning from deliberate deception.
Sources and reference material
- Reuters, 2 November 2026: Ukraine says public air raid alert app sent false alerts after being hacked
- ENISA, 22 September 2026: ENISA Threat Landscape 2026
- World Economic Forum, 12 January 2026: Global Cybersecurity Outlook 2026
- FBI and EPA, 30 July 2026: Malicious Cyber Actors Targeting Water and Wastewater Sector Internet-Facing Programmable Logic Controllers
- NSA, 19 August 2026: Active Threats of Programmable Logic Controllers
- CISA, FBI, NSA and international partners, 8 October 2026: Advisory on Integrity Technology Group and critical infrastructure targeting
- CERT-In, 15 October 2026: Advisory CIAD-2026-0049: AI Agents as Attack Vectors
- Ministry of Home Affairs, Government of India, 24 March 2026: Assistance to States to Tackle Cyber Incidents
- Press Information Bureau, 23 January 2026: CERT-In: India’s Frontline Defender against Cyber Threats
Editorial note: Incident figures, dates and agency assessments are attributed to the cited sources. Cyber attribution remains subject to the evidence and qualifications stated by the reporting authorities. This article distinguishes verified incidents from assessments, allegations and broader strategic analysis.

